Buy uwccr.com ?
We are moving the project
uwccr.com .
Are you interested in purchasing the domain
uwccr.com ?
domain@kv-gmbh.de · 0541-91531010
Buy uwccr.com ?
Is SQL injection still possible in 2019?
Yes, SQL injection is still possible in 2019. Despite advancements in security measures and awareness about this vulnerability, many websites and applications are still vulnerable to SQL injection attacks. It remains a common attack vector for hackers to exploit and gain unauthorized access to databases. It is crucial for developers to implement proper input validation and parameterized queries to prevent SQL injection attacks. **
Is an SQL injection attempt punishable by law?
Yes, an SQL injection attempt can be punishable by law. In many jurisdictions, attempting to exploit vulnerabilities in computer systems, including SQL injection attacks, can be considered a criminal offense under laws related to unauthorized access to computer systems, data theft, or computer fraud. Penalties for such offenses can include fines, imprisonment, or other legal consequences. It is important for individuals to understand and comply with the laws and regulations related to computer security and data protection to avoid legal repercussions. **

Similar search terms for SQL injection
Top-Angebote
Products related to SQL injection:
-
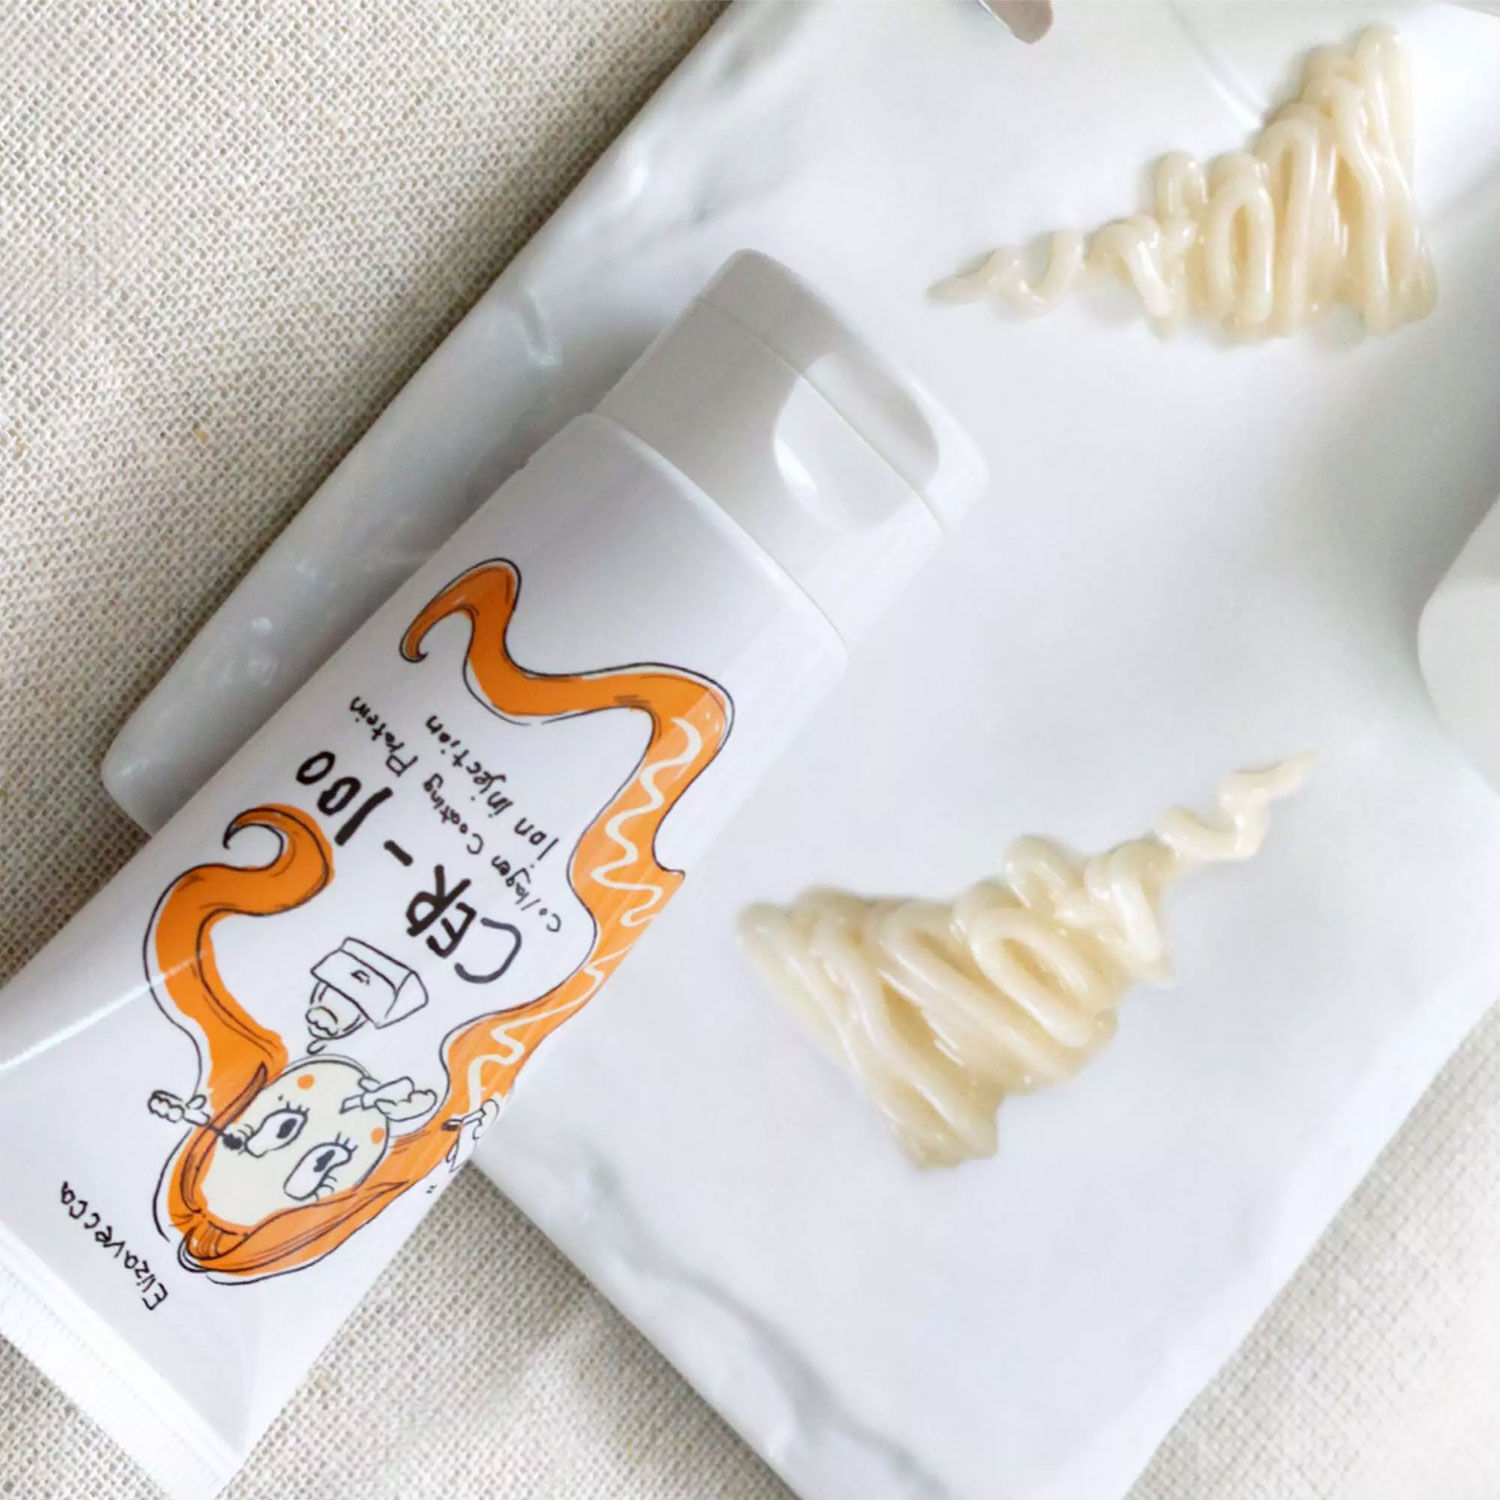
ELIZAVECCA Cer-100 Collagen Coating Protein Ion Injection 50mlElizavecca CER-100 Collagen Coating Protein Ion Injection Deep Moisturizing Hair Mask -hiusnaamio kosteuttaa ja palauttaa vaurioituneet, vaurioituneet ja vaikeasti hoidettavat hiukset, palauttaa elinvoimaa ja voimaa, jolloin hiukset ovat pehmeät, joustavat ja hallittavissa. Koostumuksen sisältämä hydrolysoitu sianlihakollageeni ravitsee hiuksia, parantaa niiden kimmoisuutta ja tekee niistä sileämmät ja kiiltävämmät. Hydrolysoitu keratiini vahvistaa hiuskuituja, parantaa hiusten rakennetta ja väh11,95 €*Shipping: 0,00 €Secure redirect to the provider
-
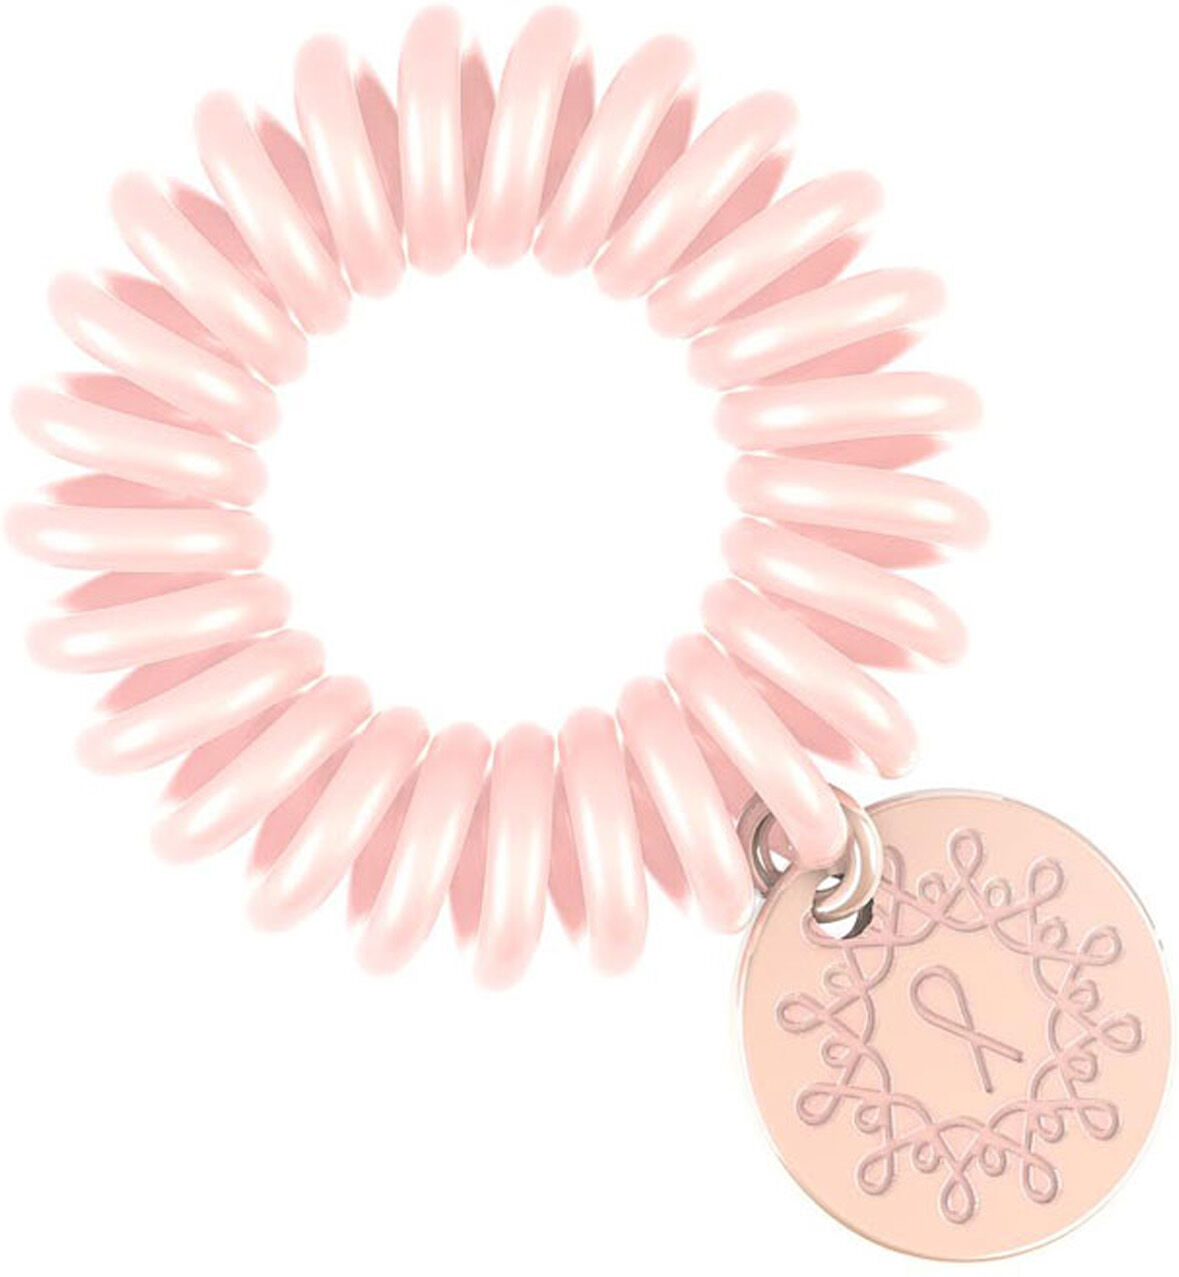
INVISIBOBBLE Original Pink Heroes Charity Edition Hair RingInvisibobble Originalin ihana puhelinjohtimen muotoilu jakaa epätasaisen paineen pateen ympärille, antaa jokaiselle yksittäiselle hiukselle tilaa ja varmistaa hiusten pysymisen yhdessä ilman liiallista jännitystä. Invisibobble ei vahingoita hiuksia, vedä yksittäisiä säikeitä tai paina päänahkaa. Sopii kaikille hiustyypeille, kiharille, suorille, paksuille tai hienoille hiuksille.1,95 €*Shipping: 0,00 €Secure redirect to the provider


-
How can one prevent SQL injection and Cross-Site Scripting?
To prevent SQL injection, one can use parameterized queries or prepared statements in their code to ensure that user input is treated as data rather than executable code. Additionally, input validation can be implemented to restrict the type and format of user input. To prevent Cross-Site Scripting, one can sanitize user input by encoding special characters and validating input fields to only allow certain types of data. Using security mechanisms like Content Security Policy (CSP) can also help prevent XSS attacks by restricting the sources from which resources can be loaded on a webpage. Regularly updating software and libraries, as well as conducting security audits, can also help prevent both SQL injection and Cross-Site Scripting vulnerabilities. **
-
Can you give me exercises on the topic of SQL injection?
Sure! Here are a few exercises you can try to practice SQL injection: 1. Use a vulnerable web application or a purposely built SQL injection lab to practice exploiting SQL injection vulnerabilities. Try to manipulate the input fields to inject SQL commands and retrieve sensitive information from the database. 2. Write your own simple web application with a vulnerable input field and try to exploit it using SQL injection. This will help you understand how SQL injection works and how to prevent it in your own code. 3. Research and practice using different types of SQL injection techniques, such as error-based, union-based, and blind SQL injection. This will give you a better understanding of the various ways attackers can exploit SQL injection vulnerabilities. Remember to always practice ethical hacking and only test on systems that you have permission to access. **
-
How can one rewrite SQL questions into SQL commands?
To rewrite SQL questions into SQL commands, one can start by identifying the specific data that needs to be retrieved or manipulated. Then, the question can be translated into SQL commands such as SELECT, INSERT, UPDATE, or DELETE, depending on the specific task at hand. It's important to ensure that the SQL commands are structured correctly and include the necessary clauses such as WHERE, GROUP BY, or ORDER BY to achieve the desired outcome. Additionally, one should consider any necessary joins or subqueries to retrieve data from multiple tables. **
-
What is better: direct injection or intake manifold injection?
Direct injection is generally considered better than intake manifold injection because it allows for more precise fuel delivery, resulting in improved fuel efficiency and power output. Direct injection also reduces the risk of carbon buildup on the intake valves, which can be a common issue with intake manifold injection. Additionally, direct injection allows for better control over the air-fuel mixture, leading to cleaner emissions. Overall, direct injection is the preferred choice for modern engines due to its superior performance and efficiency. **


What is SQL and what does an SQL server do?
SQL, or Structured Query Language, is a programming language used to manage and manipulate data in relational databases. It allows users to create, retrieve, update, and delete data from databases, as well as define and manipulate the structure of the data. An SQL server is a software application that is used to store and manage databases, allowing multiple users to access and manipulate the data concurrently. It provides a secure and efficient way to store and retrieve data, and can handle large volumes of data and complex queries. **
Is the SQL Community Server package damaged on the Fedora server?
To determine if the SQL Community Server package is damaged on the Fedora server, you can run the following command in the terminal: "sudo dnf check". This command will check for any problems with the installed packages, including the SQL Community Server package. If there are any issues with the package, the command will provide information on how to fix them. Additionally, you can also use the "rpm -V" command to verify the integrity of the SQL Community Server package files. If any files are reported as being modified or corrupted, it may indicate that the package is damaged. **
Top-Angebote
Products related to SQL injection:
-
ELIZAVECCA Cer-100 Collagen Coating Protein Ion Injection 50mlElizavecca CER-100 Collagen Coating Protein Ion Injection Deep Moisturizing Hair Mask -hiusnaamio kosteuttaa ja palauttaa vaurioituneet, vaurioituneet ja vaikeasti hoidettavat hiukset, palauttaa elinvoimaa ja voimaa, jolloin hiukset ovat pehmeät, joustavat ja hallittavissa. Koostumuksen sisältämä hydrolysoitu sianlihakollageeni ravitsee hiuksia, parantaa niiden kimmoisuutta ja tekee niistä sileämmät ja kiiltävämmät. Hydrolysoitu keratiini vahvistaa hiuskuituja, parantaa hiusten rakennetta ja väh11,95 €*Shipping: 0,00 €Secure redirect to the provider
-
Is SQL injection still possible in 2019?
Yes, SQL injection is still possible in 2019. Despite advancements in security measures and awareness about this vulnerability, many websites and applications are still vulnerable to SQL injection attacks. It remains a common attack vector for hackers to exploit and gain unauthorized access to databases. It is crucial for developers to implement proper input validation and parameterized queries to prevent SQL injection attacks. **
-
Is an SQL injection attempt punishable by law?
Yes, an SQL injection attempt can be punishable by law. In many jurisdictions, attempting to exploit vulnerabilities in computer systems, including SQL injection attacks, can be considered a criminal offense under laws related to unauthorized access to computer systems, data theft, or computer fraud. Penalties for such offenses can include fines, imprisonment, or other legal consequences. It is important for individuals to understand and comply with the laws and regulations related to computer security and data protection to avoid legal repercussions. **
-
How can one prevent SQL injection and Cross-Site Scripting?
To prevent SQL injection, one can use parameterized queries or prepared statements in their code to ensure that user input is treated as data rather than executable code. Additionally, input validation can be implemented to restrict the type and format of user input. To prevent Cross-Site Scripting, one can sanitize user input by encoding special characters and validating input fields to only allow certain types of data. Using security mechanisms like Content Security Policy (CSP) can also help prevent XSS attacks by restricting the sources from which resources can be loaded on a webpage. Regularly updating software and libraries, as well as conducting security audits, can also help prevent both SQL injection and Cross-Site Scripting vulnerabilities. **
-
Can you give me exercises on the topic of SQL injection?
Sure! Here are a few exercises you can try to practice SQL injection: 1. Use a vulnerable web application or a purposely built SQL injection lab to practice exploiting SQL injection vulnerabilities. Try to manipulate the input fields to inject SQL commands and retrieve sensitive information from the database. 2. Write your own simple web application with a vulnerable input field and try to exploit it using SQL injection. This will help you understand how SQL injection works and how to prevent it in your own code. 3. Research and practice using different types of SQL injection techniques, such as error-based, union-based, and blind SQL injection. This will give you a better understanding of the various ways attackers can exploit SQL injection vulnerabilities. Remember to always practice ethical hacking and only test on systems that you have permission to access. **
Similar search terms for SQL injection
-
INVISIBOBBLE Original Pink Heroes Charity Edition Hair RingInvisibobble Originalin ihana puhelinjohtimen muotoilu jakaa epätasaisen paineen pateen ympärille, antaa jokaiselle yksittäiselle hiukselle tilaa ja varmistaa hiusten pysymisen yhdessä ilman liiallista jännitystä. Invisibobble ei vahingoita hiuksia, vedä yksittäisiä säikeitä tai paina päänahkaa. Sopii kaikille hiustyypeille, kiharille, suorille, paksuille tai hienoille hiuksille.1,95 €*Shipping: 0,00 €Secure redirect to the provider
-
How can one rewrite SQL questions into SQL commands?
To rewrite SQL questions into SQL commands, one can start by identifying the specific data that needs to be retrieved or manipulated. Then, the question can be translated into SQL commands such as SELECT, INSERT, UPDATE, or DELETE, depending on the specific task at hand. It's important to ensure that the SQL commands are structured correctly and include the necessary clauses such as WHERE, GROUP BY, or ORDER BY to achieve the desired outcome. Additionally, one should consider any necessary joins or subqueries to retrieve data from multiple tables. **
-
What is better: direct injection or intake manifold injection?
Direct injection is generally considered better than intake manifold injection because it allows for more precise fuel delivery, resulting in improved fuel efficiency and power output. Direct injection also reduces the risk of carbon buildup on the intake valves, which can be a common issue with intake manifold injection. Additionally, direct injection allows for better control over the air-fuel mixture, leading to cleaner emissions. Overall, direct injection is the preferred choice for modern engines due to its superior performance and efficiency. **
-
What is SQL and what does an SQL server do?
SQL, or Structured Query Language, is a programming language used to manage and manipulate data in relational databases. It allows users to create, retrieve, update, and delete data from databases, as well as define and manipulate the structure of the data. An SQL server is a software application that is used to store and manage databases, allowing multiple users to access and manipulate the data concurrently. It provides a secure and efficient way to store and retrieve data, and can handle large volumes of data and complex queries. **
-
Is the SQL Community Server package damaged on the Fedora server?
To determine if the SQL Community Server package is damaged on the Fedora server, you can run the following command in the terminal: "sudo dnf check". This command will check for any problems with the installed packages, including the SQL Community Server package. If there are any issues with the package, the command will provide information on how to fix them. Additionally, you can also use the "rpm -V" command to verify the integrity of the SQL Community Server package files. If any files are reported as being modified or corrupted, it may indicate that the package is damaged. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.